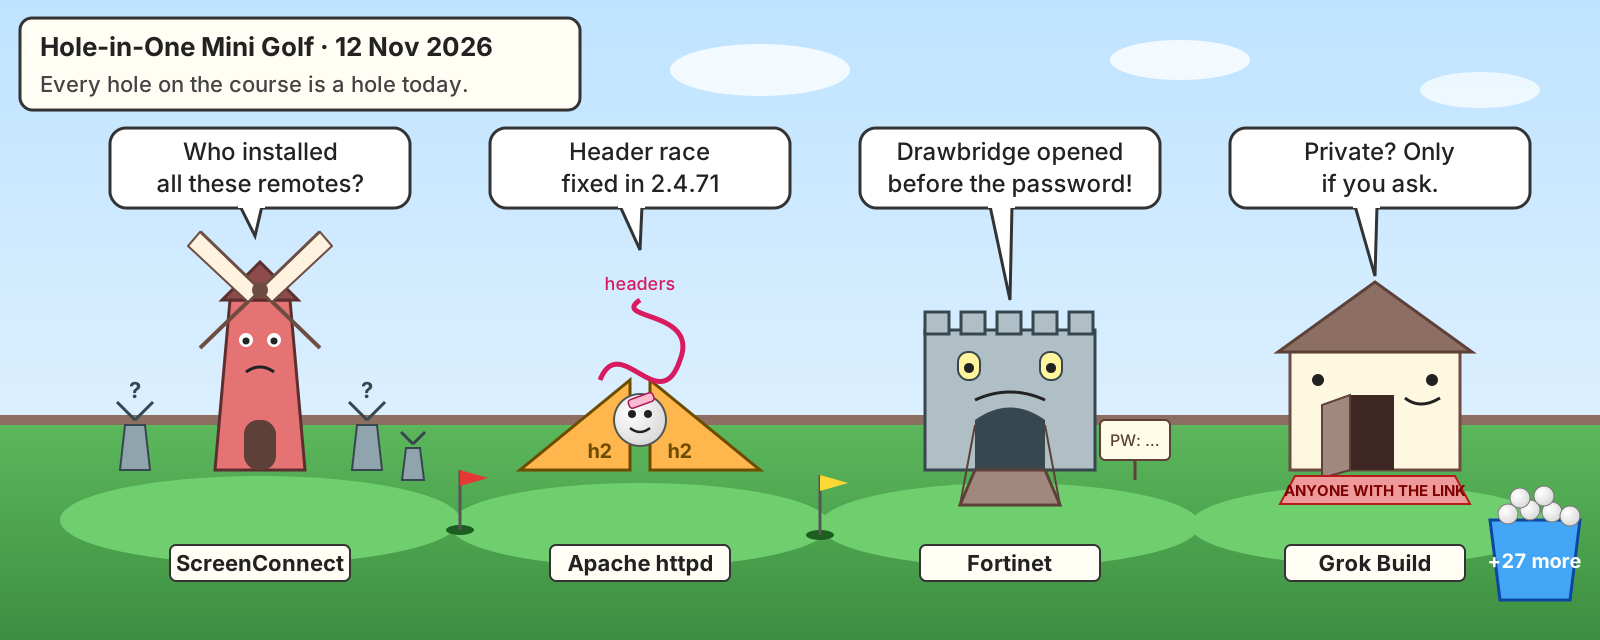
The day’s biggest story is a live campaign against MSPs. Attackers have got into ScreenConnect partner environments and are using them to install their own remote-access clients on customer machines, and ConnectWise has disabled a family of third-party extensions across about 400 partner environments. Apache shipped httpd 2.4.71 for a critical mod_http2 bug that can lead to remote code execution, and Fortinet released two unauthenticated critical fixes for FortiOS and FortiManager. On the AI side, a study found more than 35,000 Grok-built apps open to anyone with the address, and Microsoft researchers showed that editing fewer than 10 neurons can backdoor an agent model.
Do today
- ScreenConnect (cloud and on-premises partners): review Run Command history, extension installs and admin activity, even without alerts. On-premises servers must disable Labtech Plus, RMM Plus, RMM+ and both Password Link variants by hand, and must not reinstall them. (ConnectWise advisory)
- Apache HTTP Server 2.4.55–2.4.70 with mod_http2: upgrade to 2.4.71. If you can’t do that today, turn off HTTP/2 (
Protocols http/1.1) on internet-facing hosts. (Apache httpd 2.4 vulnerabilities) - FortiManager and FortiOS: upgrade FortiManager to 7.2.9, 7.4.6, 7.6.8 or 8.0.1, and FortiOS to 7.2.14, 7.4.13, 7.6.8 or 8.0.2. Fortinet lists no workaround for either flaw. Until the upgrade, keep FGFM ports off untrusted networks. (FG-IR-26-275, FG-IR-26-267)
- KEV deadlines today and tomorrow: OpenSSH CVE-2026-123158, FreeSWITCH CVE-2026-116779, IBM Aspera Faspex CVE-2026-123218 and GPUStack CVE-2026-102895 are due today. Barracuda CVE-2026-116606 and CVE-2026-111560, and Ivanti Connect Secure CVE-2026-118527, are due 13 November. (CISA KEV feed)
- Plone sites (4.3 through 6.2): install
Products.PloneHotfix20261110or the fixed packages. The chain gives anonymous visitors code execution. (Plone announcement on oss-security) - Node.js servers: move to 22.23.5, 24.22.3 or 26.13.1. Prioritise HTTP/2 and mTLS servers. (Node.js November 2026 security releases)
AI and agent security5 stories
- Claroc: 35,578 Grok-built apps open to anyone, about 1 in 10 holding internal or personal data — Claroc checked 37,571 live apps built with Grok Build on 8 November and found 94.7% opened without sign-in. Exposed apps include a hospital group’s staff directory with more than 3,500 entries, a contractor’s timesheet app with plaintext passwords, and 24 apps built by SpaceXSI and X staff. In the researchers’ paid account, the publish panel had “Anyone with the link” pre-selected. Each app also gets its own hostname, which passive DNS can expose. In one test app, Grok-generated sign-in code added any Google account to the team before checking membership. SpaceXSI removed its staff’s apps, says employee accounts default to “Only you”, and hasn’t said it will tell other owners. Our take: an unguessable URL is not access control. Find vibe-coded apps on your domains through DNS and proxy logs, and require company-domain sign-in. (Claroc research)
- Arctic Wolf: AntiFox agent platforms on Alibaba Cloud used to reach AWS production secrets — Arctic Wolf Labs links self-hosted instances of AntiFox, a Chinese-language fork of the ARTEX agentic pentest framework, to several intrusions. In one, an ASPX webshell on IIS read
web.configconnection strings and copied config files into a public upload folder. In others, valid AWS keys or an assumed EC2 role ran hundreds of List/Get/Describe calls across about 20 services in 30 minutes. Most calls were denied, but someGetSecretValuecalls succeeded. Amazon says its services worked as designed and the credentials came from compromised customer apps. Our take: alert on a successful secret read that follows a burst of denials, not only on the denials. Arctic Wolf’s own advice applies too: don’t assume a mostly-denied sequence failed. (Arctic Wolf Labs report) - Microsoft Research: editing fewer than 10 neurons plants a sleeper backdoor in an agent model — The “Lazarus” technique changes a handful of rarely used neurons, without retraining, so the model outputs an attacker’s command when a trigger string appears, and an agent may run it. The edited model still passes normal evaluations, and the edit needs only enough RAM to run the model. Microsoft says it has not seen attackers use this. It recommends diffing checkpoints against their declared base model, taking weights only from the original publisher, and keeping approved models in a private registry. Our take: treat third-party fine-tunes, merges and quantisations like unsigned binaries. Least privilege and human approval for high-impact agent actions limit the damage when a weight check misses. (Microsoft Security blog)
- AWS mcp-gateway-registry: privilege escalation to registry admin, and an SSRF that survives the first fix — In CVE-2026-100307 (fixed in 1.25.0), the
/api/servers/*management routes checked authentication but not authorisation. Any low-privileged user could import a group mapping that made them admin and then read stored server credentials. In CVE-2026-125926 (fixed in 1.35.0), anyone who can register a server can point its upstream at internal services and sometimes read the replies. AWS warns that upgrading doesn’t undo existing state. After upgrading, checkgroup_mappingsinmcp_scopesand review every registered upstream URL. Our take: MCP gateways hold every downstream credential, so treat them like a secrets vault, with egress allow-lists and IMDSv2. (AWS bulletin 2026-179, AWS bulletin 2026-180)CVSS not published (AWS)EPSS not yet scoredKEV no - Corelight: “pinned” MCP servers kept changing their dependencies on every launch — One MCP server, pinned to a single release and commit, ran with 15 different dependency sets over five weeks. 23 of its 69 packages changed version with no configuration change, because the
uvxlauncher ignored the maintainer’s hash-pinned lock file. Of 35 MCP servers reviewed, 23 recommend an install that resolves fresh from a public registry. On one admin workstation, those servers made more than 1,600 connections to 11 management systems, including the firewall and SIEM. Our take: freeze any MCP server that holds credentials. Install once from a hash-pinned lock into its own environment, launch it directly, and give someone the job of re-locking it on a schedule. (Corelight research)
Application security6 stories
- Apache httpd 2.4.71: critical mod_http2 heap corruption can lead to RCE (CVE-2026-119618) — Released 11 November, 2.4.71 fixes a race in mod_http2’s
assign_headers()that Apache rates critical and says can lead to remote code execution. It affects 2.4.55 through 2.4.70, and the standalone mod_h2 module from 2.0.8 through 2.0.42. The same release fixes an important mod_md NULL dereference that crashes child processes (CVE-2026-106023, back to 2.4.30) and a low-severity one-byte overwrite in mod_vhost_alias (CVE-2026-109163). NVD has no CVSS score yet, and nobody has reported exploitation. Our take: check whether HTTP/2 is actually enabled (Protocols h2) on your hosts, and confirm that distro backports have arrived before you mark hosts fixed. (Apache httpd 2.4 vulnerabilities, NVD CVE-2026-119618)CVSS not yet published (NVD)Apache: criticalEPSS not yet scoredKEV no - Node.js 22.23.5, 24.22.3 and 26.13.1 fix 16 CVEs, seven of them High — The batch is mostly HTTP/2 and TLS bugs. Two HTTP/2 flaws can send freed or heap memory back to the peer (CVE-2026-123866, CVE-2026-123864). TLS 1.2 renegotiation can change the servername and bypass client-certificate authentication (CVE-2026-123872), and CA-only SNI overrides fail open to the default CA (CVE-2026-123867). Remote unauthenticated crashes complete the set. llhttp, undici and sqlite are also updated. Our take: anything relying on per-host mTLS in Node should be patched this week. Proxies that terminate HTTP/2 in front of Node reduce exposure but don’t remove it. (Node.js security releases)
Severity High (Node.js)EPSS not yet scoredKEV no - Plone: an unauthenticated chain to remote code execution, with a hotfix back to 4.3 — The Plone team released fixes on 10 November across Products.CMFPlone, CMFEditions, MimetypesRegistry, plone.batching and plone.restapi. Four are rated critical, and together they let an anonymous visitor run code on the server. Fixed CMFPlone versions are 6.2.3, 6.1.6 and 6.0.16.
Products.PloneHotfix20261110covers 4.3 through 6.2 on Python 2.7 and 3. CVEs have been requested but not yet assigned. Our take: Plone sits in many government and university estates that patch slowly, so apply the hotfix first and plan the package upgrade afterwards. (Plone announcement on oss-security) - Zoom Workplace for Windows: unauthenticated network privilege escalation rated 9.6 (CVE-2026-108186) — Zoom’s bulletin ZSB-26023 describes improper input validation in Workplace for Windows 7.1.0 through 7.1.7. It is fixed in 7.1.8. The vector requires user interaction, which tempers the network-reachable rating. A second bulletin, ZSB-26024, covers an 8.1 origin-validation flaw fixed in 7.1.5 (CVE-2026-108187). Zoom doesn’t report exploitation. Our take: push 7.1.8 through your software-distribution tooling rather than relying on in-app updates, which users can defer. (Zoom ZSB-26023, Zoom ZSB-26024)
CVSS 9.6 (v3.1, Zoom)EPSS not yet scoredKEV no - X.Org server 21.1.26 and Xwayland 24.1.15 fix eight memory-safety bugs — Three can write out of bounds: crafted EDID data from a malicious monitor (CVE-2026-109091), a wraparound in the XvShmPutImage bounds check (CVE-2026-109092), and a stack overflow in XTestFakeInput (CVE-2026-109093). The rest are 32-bit integer overflows and size checks in XRes, glamor and Xv that cause out-of-bounds reads or crashes. No CVSS scores were published. This follows 12 fixes a month ago. Our take: on multi-user and VDI hosts the X server is a local privilege boundary, so take the distro backports. (X.Org advisory on oss-security)
- Emacs 31.1: a repository’s
.dir-locals.elcould run code when you open a file — Emacs 31.1 didn’t validate modes supplied through directory-local variables before applying them, and the issue was reported publicly with a patch. 30.2 is not affected, and the fix will ship in 31.2. No CVE has been assigned yet. Our take: this is the same “opening a cloned repo runs code” risk that hits coding agents and IDEs. Until 31.2 ships, apply the patch or open untrusted checkouts withenable-local-variablesset to nil. (Emacs advisory on oss-security)
Exploited and critical CVEs5 stories
- KEV: no additions since 10 November; four deadlines today and three tomorrow — The catalogue is still at version 2026.11.10. Today’s 12 November deadlines cover the OpenSSH “sshole” bypass, the FreeSWITCH SIP command injection, the IBM Aspera Faspex privilege escalation and the GPUStack auth bypass. On 13 November the Barracuda ESG pair (CVE-2026-116606, CVE-2026-111560) and Ivanti Connect Secure CVE-2026-118527 fall due. Outlook CVE-2026-124194, Chrome CVE-2026-125350, Cisco BroadWorks and Openwave are due 24 November. Our take: the Barracuda pair has a three-day deadline because it is being chained pre-auth to root, so close it first. (CISA KEV feed, CISA KEV alert, 10 November)
- FortiManager: crafted FGFM packets run commands before the registration password is checked (CVE-2026-126261) — Fortinet rates this improper-authorisation flaw 9.0. An unauthenticated attacker who can reach the FGFM port can execute code. Affected versions are 7.2.0–7.2.8, 7.4.0–7.4.5, 7.6.0–7.6.7 and 8.0.0. Fortinet lists no workaround and says it is not known to be exploited. It is one of three criticals in a 10 November release of about 90 advisories. Another critical is an authorisation bypass in the FortiAnalyzer/FortiManager dmserver (CVE-2026-126229). Our take: FGFM is the channel managed devices use to reach FortiManager, so it is often reachable from branch networks or the internet. Treat any instance where it is as urgent. (FG-IR-26-275, FortiGuard PSIRT)
CVSS 9.0 (v3, Fortinet)EPSS not yet scoredKEV no - FortiOS and FortiSASE: an unauthenticated attacker can inject OSPF link-state advertisements (CVE-2026-126253) — Fortinet rates this 9.3. It is an authentication bypass in the OSPF daemon that lets crafted requests broadcast LSAs, which means poisoned routes. Fixes are in 7.2.14, 7.4.13, 7.6.8 and 8.0.2. FortiOS 7.0 and several FortiSASE trains must migrate to a fixed release, and there is no workaround. Fortinet credits its internal product security team, which found the bug with the help of an AI model. Our take: impact depends on OSPF being enabled on an interface an attacker can reach. Check where adjacency is allowed and require OSPF authentication while you schedule upgrades. (FG-IR-26-267)
CVSS 9.3 (v3, Fortinet)EPSS not yet scoredKEV no - Ivanti November batch: Endpoint Manager SQL injection and an unauthenticated CSA certificate flaw — Ivanti published advisories for Endpoint Manager, Cloud Services Application, Sentry, EPMM and User Workspace Manager on 10 November and says none are exploited. SecurityWeek reports an EPM SQL injection leading to unauthenticated RCE rated 9.8 (CVE-2026-121653, fixed in EPM 2024 SU8). It also reports a 9.4 missing-authentication bug in CSA (CVE-2026-121683, fixed in CSA 5.0.8.1) that lets attackers add or delete trusted EPM Core certificates, though Dual NIC setups aren’t exposed externally. Ivanti’s advisory pages did not load for us, so those scores and versions are unconfirmed. Our take: EPM is a management plane with domain-wide reach, so patch it ahead of the Sentry fixes. (Ivanti November 2026 security update, SecurityWeek)
CVSS 9.8 / 9.4 (SecurityWeek, unconfirmed)EPSS not yet scoredKEV no - Hyperglass looking-glass servers: researchers report trivial pre-auth RCE at ISPs and hosts — A 10 November oss-security post says the open-source network looking-glass has OS command-execution flaws that easily become unauthenticated remote code execution. It notes that many ISPs and hosting providers expose hyperglass to the internet. The post gives no affected versions, CVE or fix status, and links to the researchers’ write-up. Our take: a looking glass usually sits next to routing infrastructure and runs commands against it, so code execution there is worth more than the web page suggests. Put it behind authentication or an allow-list until a fixed release is confirmed. (oss-security post)
Cloud and infrastructure5 stories
- ScreenConnect: attackers use MSP consoles to install their own remote-access clients on customer machines — ConnectWise confirmed unauthorised access to some partner ScreenConnect environments. Attackers used Run Command to deploy rogue ScreenConnect clients that report outside the MSP. ConnectWise says it found no compromise of its own infrastructure and no ScreenConnect vulnerability. Its current view is that third-party extensions in the RMM+ family were abused, and it has disabled them in about 400 partner environments. Huntress’s count, as reported, is six MSPs and about 286 endpoints across 47 organisations. The Hacker News reports 288 endpoints across 48, and both counts are still rising. Our take: disabling the extensions doesn’t remove clients that are already planted. Inventory ScreenConnect instances by client ID, and investigate infected hosts with separate tooling, not interactive sessions. (ConnectWise advisory, BleepingComputer, The Hacker News)
- Xen XSA-529: a timing leak lets unauthenticated attackers recover the XAPI pool secret (CVE-2026-102705) — XAPI compares the pool secret, the bearer token that pool hosts use to authenticate to each other, with a function whose timing depends on the data. An attacker who can reach XAPI may infer it and gain full control of the pool. All XAPI versions are affected, and there is no mitigation besides the patch. After every member is patched, rotate the secret with
xe pool-secret-rotate. Citrix’s XenServer update CTX697316 covers this alongside five other XAPI issues (XSA-530). Our take: XAPI management should never face untrusted networks. The rotation step matters because a secret already leaked outlives the patch. (Xen XSA-529)CVSS not publishedEPSS not yet scoredKEV no - eMudhra revokes eight more intermediates, says it will leave public TLS, and explains the key bug — eMudhra’s incident report traces the problem to a custom Python script used in its April 2025 key ceremony. The script read CA private keys back to the host and re-created them, cutting eight ECDSA keys down to their first byte. It handled eight RSA keys in host memory, which eMudhra says it can’t show met its CPS, so those G2B/G2C intermediates were revoked on 7 November. eMudhra will stop G1 issuance on 16 November, exit the public TLS business, and expects an independent review by 4 December. Community reviewers are pressing on the undisclosed FIPS-mode deviation and on why the June 2025 CRL anomaly wasn’t investigated. Our take: pull any pinned eMudhra intermediates and check that trust stores in appliances and containers picked up the distrust. (Mozilla Bugzilla 2083449)
- Ubuntu 26.10’s curl now checks certificate revocation locally, and OpenSSL is planned for 27.04 — Canonical has integrated upki, which builds a local CRLite-based revocation set that a systemd timer refreshes every six hours, so the check adds no network requests. In Canonical’s test, curl on 26.04 accepted a revoked certificate that 26.10 refused. Canonical plans to add the check to OpenSSL in 27.04, which would cover most software that links it. Our take: revocation that works offline matters in weeks like this one, when CAs revoke intermediates. Until the first data download completes, curl behaves as before. (Ubuntu Discourse)
- OpenSSL pre-announces five Low-severity fixes in QUIC, AES-GCM-SIV and CMS, due 1 December — Two QUIC bugs leak stack data or cause a use-after-free read in clients. Two AES-GCM-SIV bugs can drop earlier AAD from authentication or over-read on short IVs. A CMS bug loops forever on an EC recipient certificate with group order 1. Fixed releases will be 4.1.1, 4.0.4 and 3.5.10. 3.0, 1.1.1 and 1.0.2 are affected only by the CMS issue, and the FIPS modules by none. Our take: nothing here is urgent, but if you use AES-GCM-SIV with streaming AAD, review how you call it before the fix lands. (OpenSSL advisory on oss-security)
Crypto and Web35 stories
- Initia hit again: a cloud-key compromise leads to forged rollup withdrawals and a second chain halt in three weeks — SlowMist’s incident database records an Initia loss on 10 November from a private-key leak, at $615,000. Reports citing Initia’s later statement say the attacker got in through command injection on 9 November and used a compromised Google Cloud key to approve forged IBC withdrawals from five rollups’ escrow. Those reports put about $3.27 million moved, with about $2.16 million still on the halted chain. We could not load Initia’s own post, so treat the $3.27 million figure and the root cause as unconfirmed. The two figures may measure different things: what left the chain versus what moved out of escrow. Initia’s first incident, a MoveVM bug on 23 October, cost about $2.7 million. Our take: rollup operators that hold signing authority in cloud projects need the same key isolation as bridge validators, because an environment-variable leak shouldn’t be able to approve withdrawals. (SlowMist Hacked database)
- Across Protocol: domain hijacked through registrar social engineering, users sent to a phishing page — SlowMist’s database lists a 10 November social-engineering incident at Across, with no loss figure. Press reports say attackers took across.to through its registrar and served a page asking users to sign approvals and permits, starting about 18:45 UTC. Across reportedly said its contracts and API integrations were unaffected and that it will compensate users. GoPlus’s estimate of about $350,000 drained across six chains is unconfirmed by Across. Our take: front-ends are now the softest target for bridges. Registrar lock, registry lock and DNSSEC are cheap, and wallet teams should warn on fresh unlimited approvals to a bridge’s spender. (SlowMist Hacked database, FinanceFeeds)
- Mercado Bitcoin: the attacker’s 106 BTC still hasn’t moved, and loss counts range from $36 million to $49 million — On-chain, the attacker’s Bitcoin address has received 106.07 BTC and spent nothing. Rekt’s reconstruction, based on Bitquery data, puts the gross haul at $48.6 million across 11 chains, including a sweep of about 36,000 customer deposit addresses. The exchange’s own figures have ranged from about $38 million to $36.3 million. Bitquery counts $11.8 million frozen by stablecoin issuers, while the exchange says more than $15 million is blocked. Mercado Bitcoin began a phased reopening on 9 November and is backfilling customer balances from its own funds. It still hasn’t named the compromised system. Our take: until the exchange says otherwise, don’t send funds to old Mercado Bitcoin deposit addresses, because the deposit keys may share a compromised root. (mempool.space address record, Rekt)
- Chainalysis restores Data Solutions, completing its post-breach reconnection — Chainalysis’s incident page says Data Solutions came back online on 10 November, three days after Reactor, KYT and Address Screening returned. Customers have to reconnect using emailed instructions and enhanced security controls. The company still hasn’t published a root-cause report for the 30 October breach, which reached live API tokens for all users. Our take: compliance teams that paused screening or used fallback lists should reconcile any transactions they cleared during the outage window. (Chainalysis incident updates)
- Smaller incidents this week: Rujira AMM Strategies and $TENDRIL — SlowMist’s database records a $200,000 smart-contract loss at Rujira’s AMM Strategies on THORChain on 10 November, and a $555,000 contract exploit of the $TENDRIL token on 5 November. The listings rely on the projects’ and CertiK’s own alerts, and neither project has published a post-mortem yet. Rujira’s app layer was already frozen in September after a separate FIN contract flaw. Our take: small losses like these are where new bug classes show up first, so check whether any contracts you integrate share code with these projects. (SlowMist Hacked database)
Incidents and industry5 stories
- iVerify: three-quarters of iPhone spyware detections are now criminal mass campaigns — iVerify’s 2026 Advanced Mobile Threat Report puts infections at 1.07 per 1,000 monitored devices as of October, down from 1.5 in December 2024. It says 75% of detections come from criminals using the leaked DarkSword and Coruna exploit kits through ad networks, watering holes and phishing. The kits steal passwords, messages, photos and crypto. In enterprises, each criminal detection involved an ordinary employee’s phone, and confirmed-infected iPhones did not get Apple threat notifications. Our take: a vendor-telemetry rate isn’t a population rate, but the direction is clear. Enforce minimum iOS versions for corporate access and expect no warning from Apple. (iVerify press release)
- Baker Tilly: client data taken from a third-party provider’s platform — The accounting firm’s notice says it learned on 6 September that data relating to certain clients, stored on an unnamed provider’s platform, was accessed. Its review finished on 28 October. Texas’s breach portal lists 10,456 Texans and says the data includes Social Security numbers, names and addresses. Baker Tilly offers 24 months of Experian monitoring and has not given a total count. Our take: firms that hold client tax data are a prime pretext for W-2 and refund fraud ahead of filing season, so warn finance teams now. (Baker Tilly notice)
- University of Tübingen: about 3,900 staff records pulled through a combination of vendor-recommended settings — The university says attackers used a gap created by several settings the software vendor recommended, which together exposed internal-only functions. With a username, an attacker could retrieve names, dates of birth, work email addresses, usernames and department details. Passwords and student data weren’t affected. Logs indicate no other data was taken, and a criminal complaint has been filed. Our take: when vendor defaults are combined, they need their own review. Test what an unauthenticated user can reach after each configuration change. (University of Tübingen)
- White House nominates Michael LoSapio to lead CISA — The nomination went to the Senate on 9 November. The Record reports that CISA has had no Senate-confirmed leader in this administration, and the acting director’s term formally expired on 24 September. The Record reports that it’s unclear whether the lame-duck Senate will act. If it doesn’t, the nomination would have to be resubmitted next year. Our take: leadership churn slows CISA programmes that defenders rely on, such as KEV, CPGs and incident-reporting rules, so don’t expect big policy changes before spring. (White House nominations, The Record)
- ENISA: EU index averages 71.5, but 45% of surveyed IT service providers take more than three months to patch critical systems — As reported, ENISA’s 2026 assessment of cybersecurity in the Union keeps the EU threat level at “substantial”. Member states average 71.53 out of 100 on the revised EU Cybersecurity Index. 43% of surveyed IT service management providers ran no security assessment in a year, and 37% of organisations name supply-chain risk management as the hardest NIS2 requirement. We could link ENISA’s condensed index document but couldn’t extract the survey figures from it ourselves, so they rest on Help Net Security’s reading. Our take: if your managed service providers sit in that slow-patching 45%, write patch SLAs into the contract. (ENISA condensed index (PDF), Help Net Security)
Bottom line
- Remote-management platforms are the main route in this week. Audit ScreenConnect Run Command history and extensions today, and treat any rogue client ID as a full incident.
- Today’s patch list is HTTP/2-heavy: Apache httpd 2.4.71 and Node.js both fix memory bugs in their HTTP/2 stacks. Fortinet’s FGFM and OSPF criticals need no authentication, and none of the three has a workaround besides disabling the feature.
- AI risk comes from settings and supply chains more than from the models. Grok apps are public by default, MCP launchers ignore lock files, and model weights can be edited. Inventory, pinning and least privilege address all three.